
AI adoption is exploding across enterprises—but much of it is happening outside the view of security teams. This growing phenomenon, known as shadow AI, is quickly becoming one of the most critical risks organizations face in 2026.
Below are the most important shadow AI statistics every CISO, CIO, and security leader should understand—along with what they mean for your organization.
Key Shadow AI Statistics (2026)
1. 78% of Employees Use Unapproved AI Tools
The majority of employees are already using AI tools without formal approval. AI tools are being adopted bottom-up, not top-down. Employees prioritize productivity over policy. Security teams often discover usage after the fact. What it means: Shadow AI is no longer an edge case—it's the default.
2. AI Usage Has Grown Over 60% Year-Over-Year
Enterprise AI adoption is accelerating rapidly. New AI tools and agents are emerging daily, AI is being embedded into existing workflows, and adoption is happening across every business function. What it means: Your attack surface is expanding faster than traditional controls can keep up.
3. 1 in 3 AI Interactions Involve Sensitive Data
A significant portion of AI usage involves customer data, internal documents, proprietary code, and financial or strategic information. What it means: Shadow AI is not just usage—it's data exposure risk.
4. Over 50% of Organizations Have No AI Visibility
Most enterprises cannot answer basic questions: What AI tools are being used? Who is using them? What data is being shared? What it means: Security teams are operating without visibility into one of the fastest-growing risk areas.
5. Thousands of AI Tools Are in Use Across Enterprises
Organizations are not dealing with a handful of tools—they're dealing with hundreds to thousands of AI apps, AI agents operating across workflows, and AI embedded in SaaS platforms. What it means: Manual tracking is impossible. AI inventory must be automated.
6. AI Agents Are the Fastest-Growing Risk Surface
Beyond tools, organizations are now seeing autonomous AI agents, API-connected AI workflows, and AI systems making decisions and taking actions. What it means: Shadow AI is evolving into shadow autonomy.
7. Detection Lag Can Be Weeks or Months
In many organizations, AI usage is discovered long after it begins, security reviews happen retroactively, and policies are applied too late. What it means: Real-time detection is becoming essential.
8. Traditional Security Tools Miss Most AI Activity
Legacy tools were not built for AI: SIEMs lack AI-specific context, CASBs don't identify AI behavior deeply, and endpoint tools miss browser-based AI usage. What it means: New approaches to AI security are required.
Why Shadow AI Is Growing So Fast
The data tells a clear story—but why is this happening? First, AI delivers immediate value—employees see instant productivity gains. Second, barriers to entry are low: most AI tools are free, easy to access, and require no installation. Third, governance is lagging adoption—organizations are still defining policies, understanding risks, and building frameworks. The result: usage outpaces control.
The Real Risk Behind the Numbers
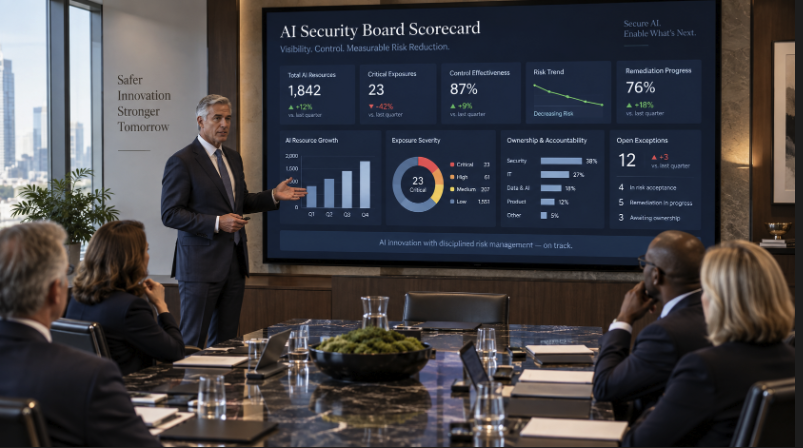
These statistics are not just trends—they represent real business risk: data leakage into AI models, unauthorized integrations with internal systems, compliance violations (GDPR, HIPAA, etc.), and untracked decision-making by AI systems. Shadow AI is not just an IT issue—it's a board-level concern.
What CISOs Need to Do in 2026
Based on these trends, leading security teams are focusing on five priorities: (1) AI Visibility First—you cannot secure what you cannot see. (2) Build a Complete AI Inventory—track every app, agent, and model. (3) Monitor AI Usage Continuously with real-time, automated, context-aware detection. (4) Implement Policy Enforcement—move beyond detection to allow, restrict, or block. (5) Align AI Governance with Business Risk, focusing on data exposure, operational impact, and regulatory compliance.
How AIBound Helps Address Shadow AI
AIBound is built to address exactly these challenges. With AIBound, organizations can discover every AI app, agent, and model in real time; build a complete AI inventory across all environments; understand how AI tools interact with data and systems; score risk automatically using the Nucleus AI engine; and enforce policies instantly—block, allow, or coach users. AIBound turns shadow AI from an unknown risk into a managed system.
Final Takeaways
Shadow AI is now widespread across enterprises. Most organizations lack visibility into AI usage. AI adoption is accelerating faster than governance. Traditional tools are not designed for AI risk. CISOs must move from detection to real-time control.
Want to Understand Your Shadow AI Exposure?
See how AIBound helps you detect shadow AI in real time, build your complete AI inventory, and enforce AI policies instantly. Visit aibound.com to get your AI inventory in under 24 hours—no agents, no network taps, no disruption.