

Artificial intelligence is moving into the enterprise faster than almost any technology before it. Developers are integrating models into applications. Business teams are adopting AI assistants. Autonomous agents are beginning to automate workflows.
Across industries, leaders are asking the same question: How do we secure AI without slowing down innovation?
Blocking AI adoption is not realistic. Employees will continue experimenting with new tools, and developers will continue building AI-powered systems. The challenge for CISOs is not stopping AI. It is governing it intelligently.
Why Traditional Governance Models Fail
Most enterprise governance models were designed for technologies that evolve slowly. New systems were introduced through formal procurement processes, architecture reviews, and deployment approvals.
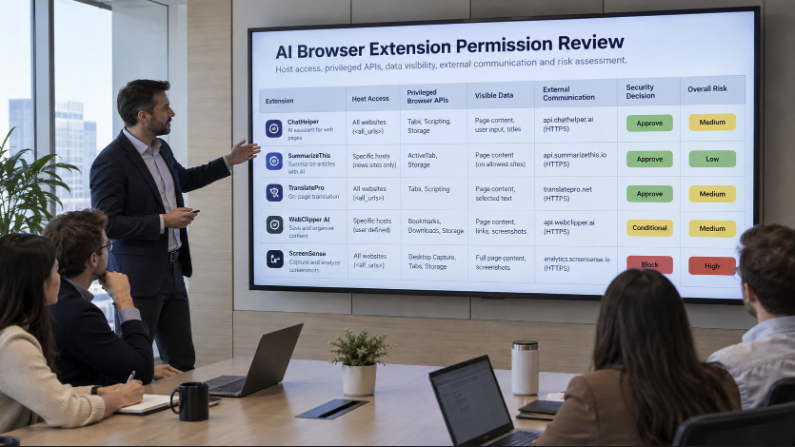
AI adoption doesn't follow that pattern. Today, AI tools can appear through browser extensions, SaaS platforms, developer frameworks, APIs, and AI agents. Many can be deployed in minutes while security review cycles take weeks.
By the time governance processes begin, AI systems may already be embedded in operational workflows.
The CISO's New Role in the Age of AI
Historically, security leaders were seen as gatekeepers. In the AI era, this model no longer works. Innovation is happening too quickly and too broadly.
Instead of acting as gatekeepers, CISOs must evolve into strategic enablers of safe AI adoption — helping organizations answer: Where is AI being used? What risks does it introduce? How do we manage those risks without slowing the business?
A Five-Step Framework for AI Governance
Organizations that successfully manage AI risk typically follow a governance model built around five core capabilities.
Step 1: Discover AI Across the Enterprise
The first step in governing AI is simple: you must know where AI exists. This includes identifying AI usage across developer environments, cloud infrastructure, SaaS platforms, employee endpoints, internal AI services, and external AI APIs.
In many organizations, this discovery process reveals far more AI activity than expected — dozens of AI-enabled SaaS tools, internal model experimentation environments, AI-powered browser extensions, and agents connected to internal APIs.
Without this visibility, governance is impossible. You cannot secure what you cannot see.
Step 2: Understand AI Access to Data and Systems
Once AI assets are identified, the next step is understanding what they can access — internal documents, enterprise databases, SaaS applications, APIs, cloud infrastructure, and automation systems.
Understanding these relationships helps answer: Which AI systems can access sensitive data? Which AI identities have privileged permissions? Which systems interact with external model providers?
Step 3: Map the AI Ecosystem
AI systems rarely operate in isolation. A single AI workflow may involve a model, a data source, an API, an automation service, and an identity controlling access.
A model connected to a database may appear safe on its own. But if that same model is exposed through an API and accessed by an external agent, the risk profile changes significantly. Mapping these relationships creates a clearer picture of the AI ecosystem.
Step 4: Prioritize Real Business Risk
Not every AI issue requires immediate attention. Security teams must prioritize AI risks based on business context — data sensitivity, identity permissions, internet exposure, regulatory requirements, and operational impact.
The most dangerous scenarios often involve toxic combinations: AI systems with privileged access to sensitive data, exposed model endpoints connected to internal resources, vulnerable dependencies in AI workloads, and automation agents interacting with production systems.
Step 5: Apply Guardrails Without Blocking Innovation
Once high-priority risks are identified, organizations must implement appropriate controls that enable safe AI usage rather than restrict innovation.
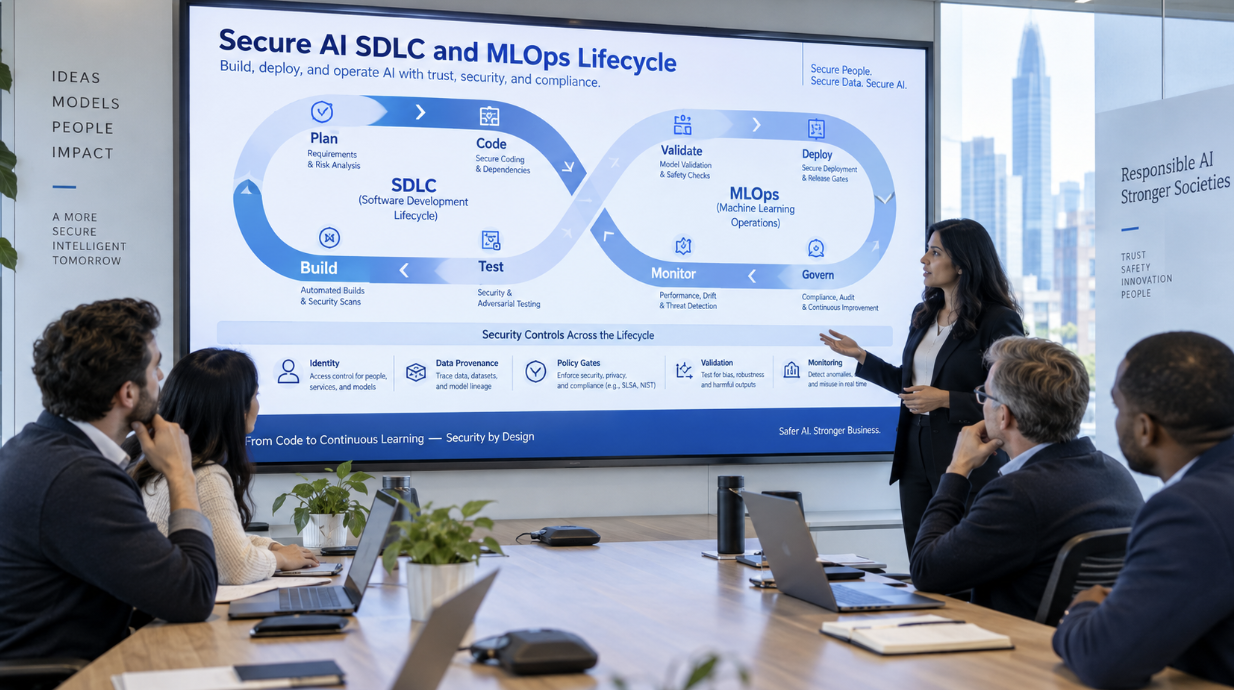
Policy controls define approved AI tools, data usage guidelines, and access permissions. Technical guardrails include monitoring AI usage, enforcing identity permissions, restricting access to sensitive datasets, and auditing AI interactions.
And continuous monitoring ensures governance remains effective as new models, tools, and integrations appear.
The Goal: Enable Safe AI Innovation
The purpose of AI governance is not to slow progress. It is to enable organizations to adopt AI confidently.
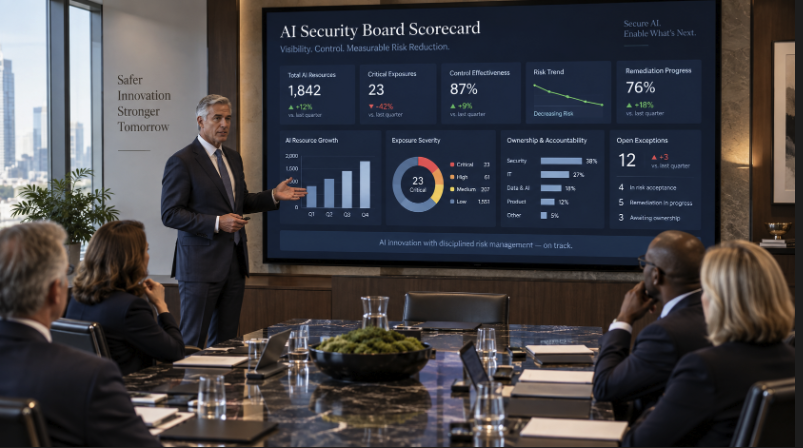
Companies that successfully implement these practices reduce the risk of data exposure, provide leadership with greater assurance, empower teams to innovate while maintaining security discipline, and build the trust required to scale AI across the organization.
The CISOs who succeed will be those who move early to establish visibility, context, and risk prioritization across their AI environments. Because in the AI era, governance is no longer about stopping innovation. It is about making innovation safe.